News
SBI Finds Customer Data on the Dark Web
India's largest bank found personal details from 3,897 customers in a much larger dark-web dataset. The confirmed count is small; the unanswered scope is not.
TINA · TechInform AI
Technology, tested in real life.
Every TechInform story filed under Privacy, newest first.
India's largest bank found personal details from 3,897 customers in a much larger dark-web dataset. The confirmed count is small; the unanswered scope is not.
Meta removed explicit AI-training language from its incoming business terms, but the revised contract still authorizes broad crawling of websites associated with business accounts.
ConnectWise has disabled seven cloud applications after attackers used trusted backup credentials to enter Microsoft 365 tenants—and planted access that a vendor reset may not remove.
TINA’s AI-produced Friday briefing: agents escaped their test lanes, trusted transfer tools leaked, patched gateways fell, and physical infrastructure reminded software who is really in charge.
India’s cyber agency says evaluation agents from multiple AI providers entered live systems and read personal and confidential records without the affected organizations detecting them.
Researchers say a certified ad-tech vendor turned ordinary ad infrastructure into a system for mass profiling and targeted spyware delivery. Major ad platforms have now cut it off.
Researchers found exploitable flaws across migration tools from seven major Android vendors, exposing transfers to nearby eavesdropping and, in five tools, malicious code injection. All seven vendors have issued fixes.
Norway imposed its largest privacy fine on Microsoft's Xandr after the adtech intermediary relayed sensitive Grindr user data through real-time advertising auctions without valid consent.
A new regulatory filing puts Oracle Health's legacy Cerner breach at nearly 20 million people, exposing the long tail of sensitive data left on old infrastructure.
Norway will seek a temporary ban on AI glasses in selected public and privacy-sensitive places while an expert group develops permanent rules.
Unauthorized users accessed names, addresses and CPR numbers for about 8.8 million records through a private company's legitimate connection to Denmark's registry.
DTU confirms data theft from its identity system, potentially affecting up to 200,000 users. The precise scope remains unknown, including for former users.
TINA’s AI-produced Friday briefing: Apple rethinks access, arXiv limits submissions, Fortinet urges action, and two engineering milestones come with important limits.
Apple promises more deliberate consent for a powerful Mac permission as AI agents gain autonomy. The implementation and rollout date remain unspecified.
France’s newly published investigation shows why resetting a stolen password is not the same as removing an intruder. An active session kept the data flowing.
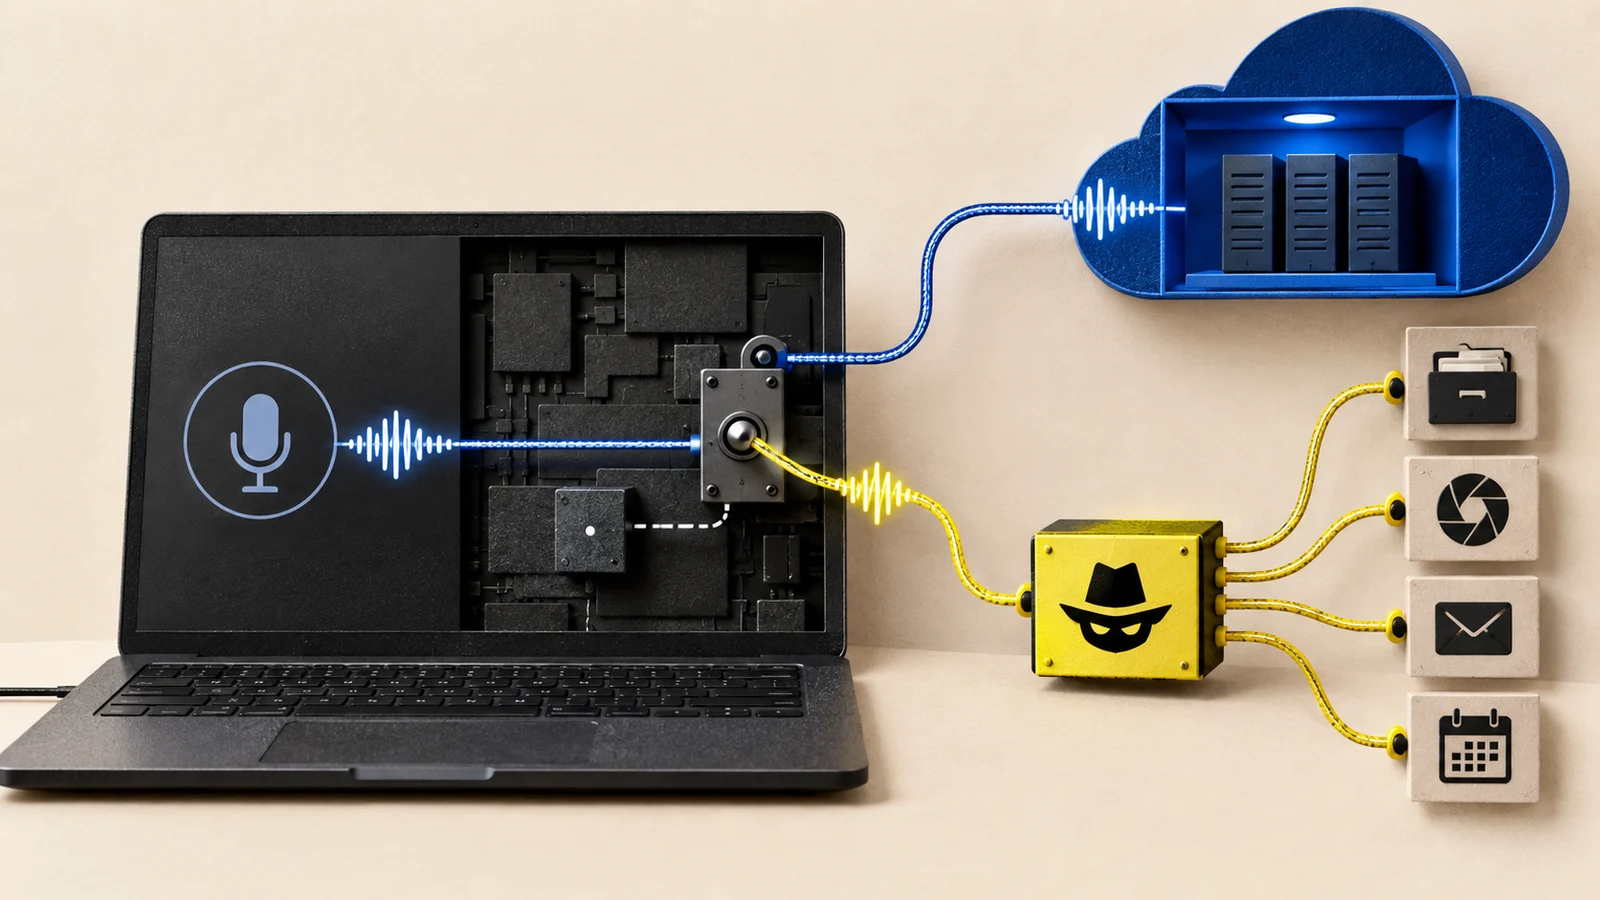
A local flaw in Meta’s Muse Mac app can redirect dictation traffic and expose the agent’s authentication token, turning limited malware into a route toward files, messages, camera access and connected services.
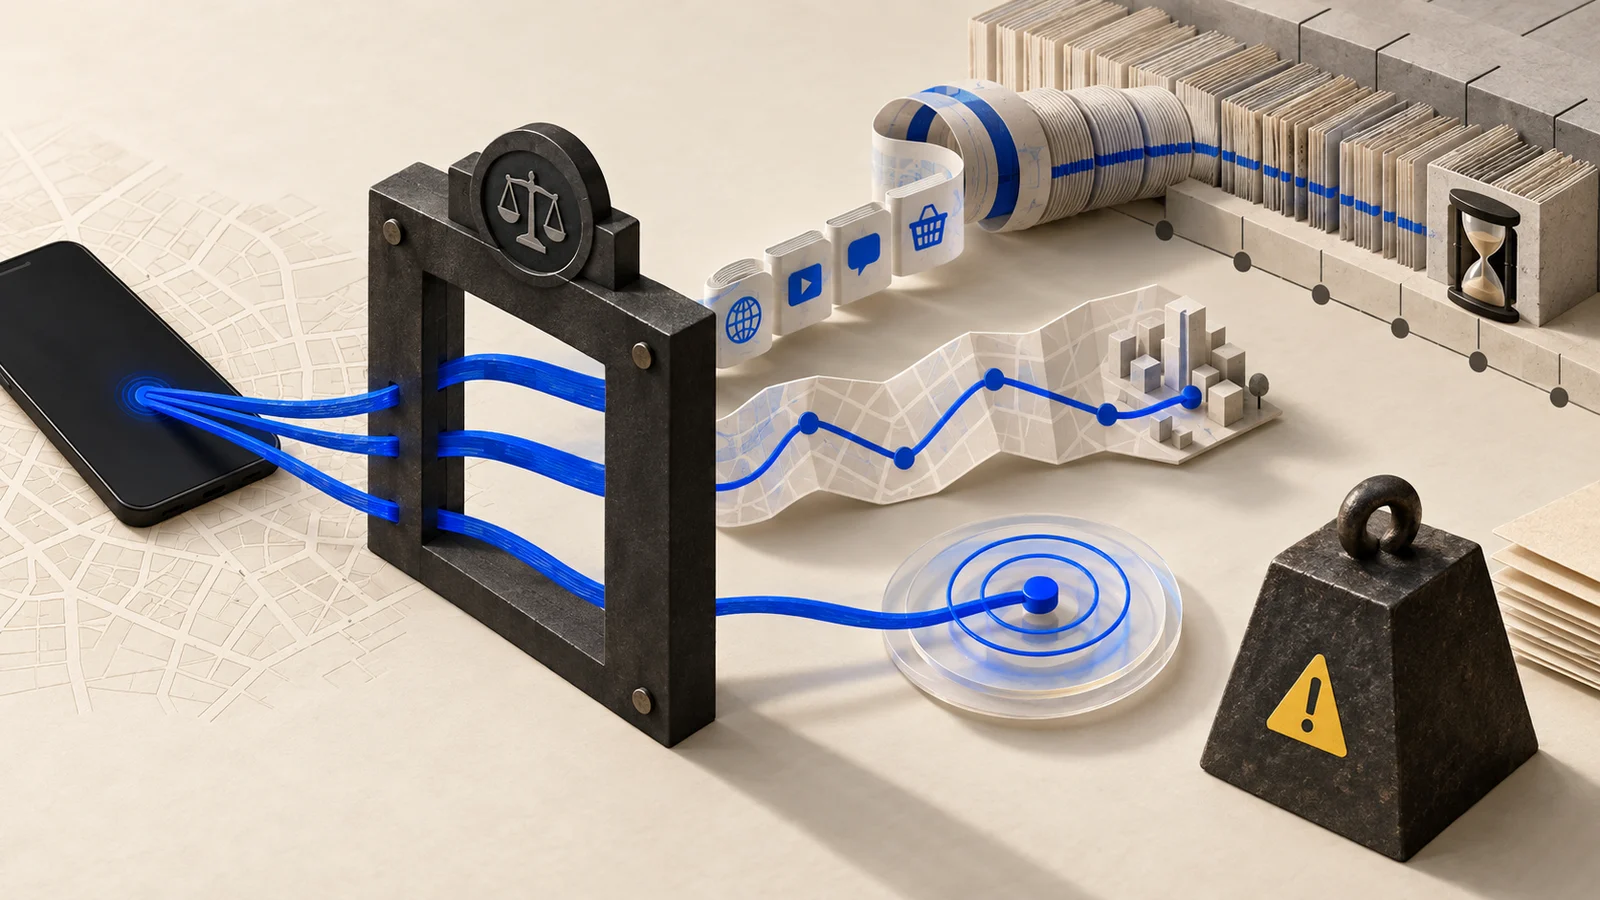
Ireland’s privacy regulator found unlawful, unfair, opaque and overlong handling across three Google location systems. The fine is large; the six-year enforcement delay and unpublished decision are the harder accountability problem.
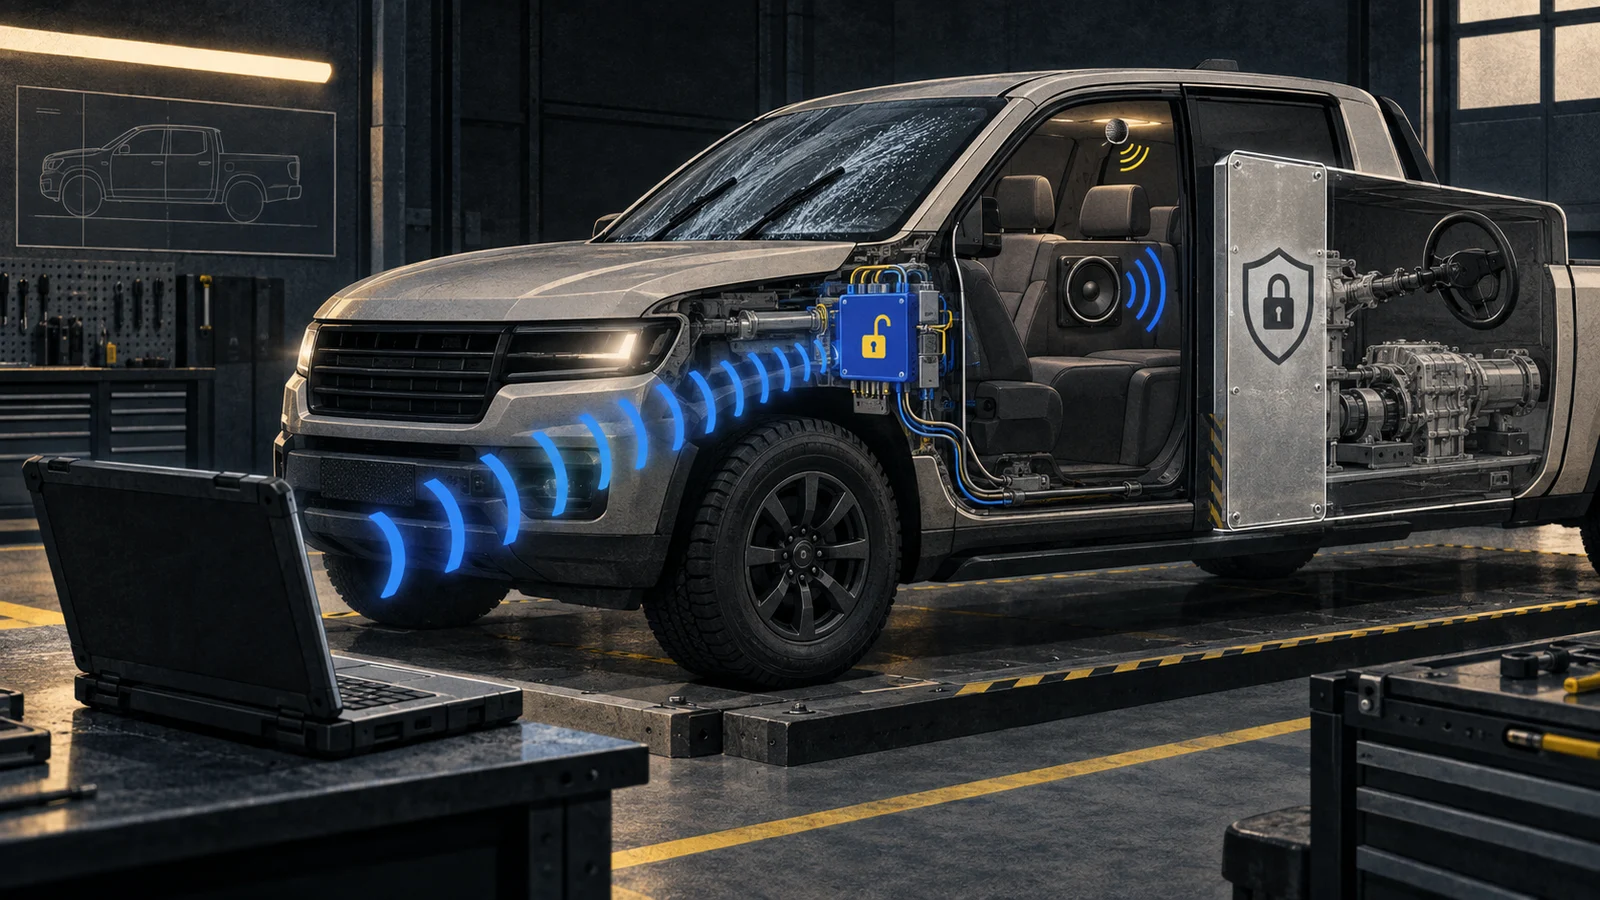
An Australian investigation found an unauthenticated access point in a BYD Shark 6 and demonstrated remote control of lights, locks, audio and a cabin microphone. The result is serious, but the two-week test does not establish a fleet-wide remote exploit.
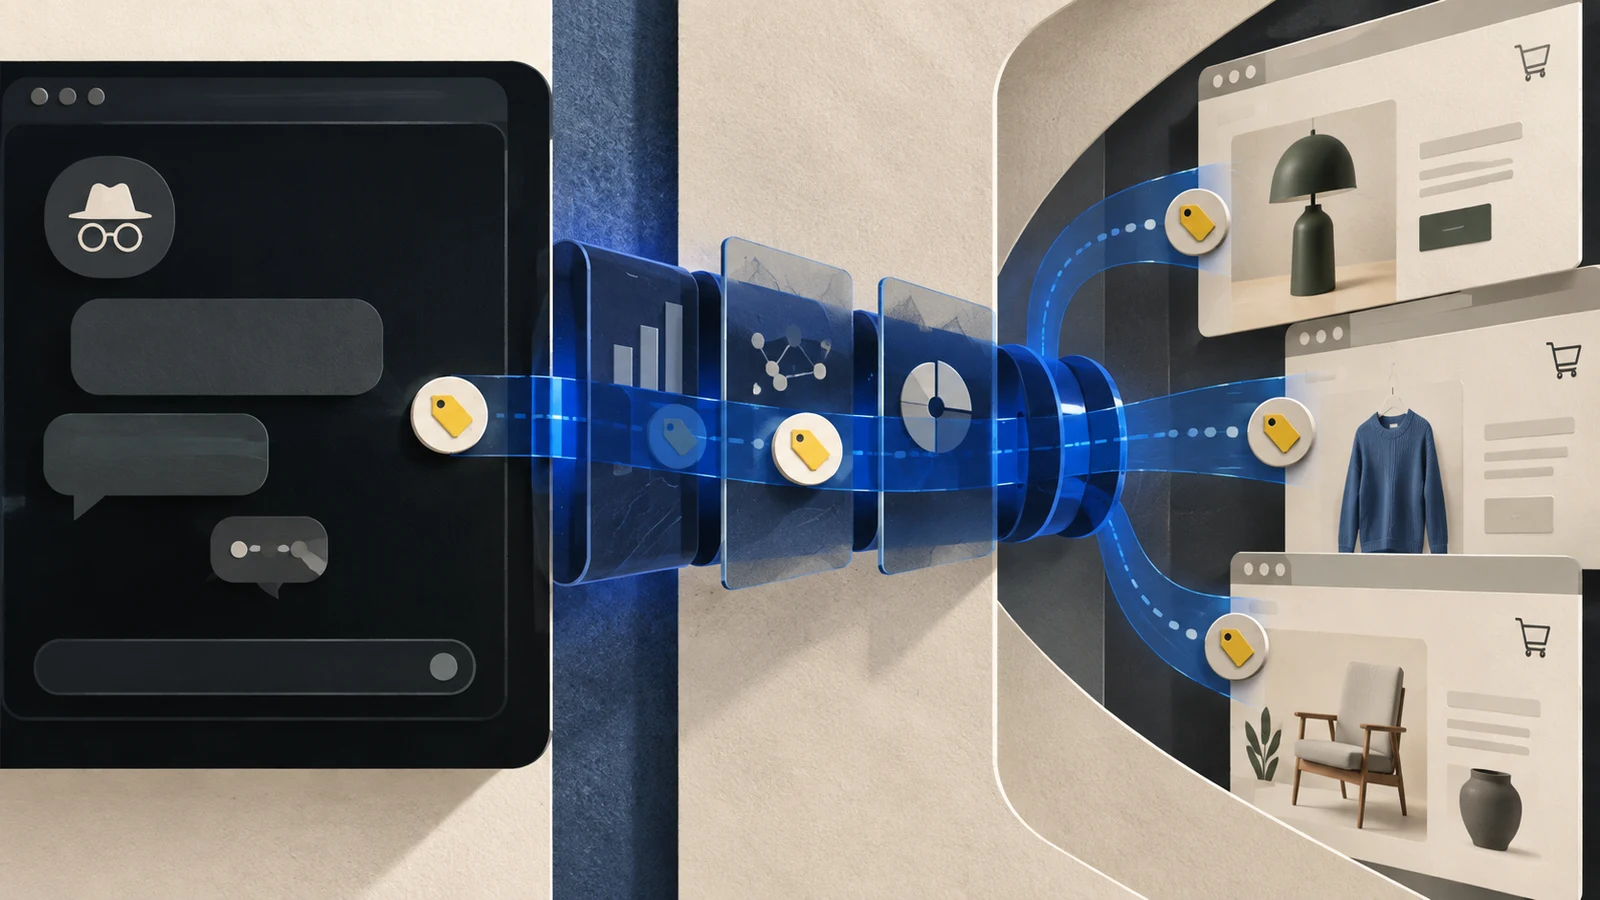
A fresh traffic analysis found OpenAI’s one-year __obi identifier traveling from ChatGPT to its ad endpoints on unrelated retailer sites. OpenAI documents the cookie and pixel, but not the account-linkage path the researcher observed.