CISA has added a WordPress Core flaw to its Known Exploited Vulnerabilities catalog, turning a recently patched weakness into a clearer warning for site owners. The agency’s November 3 entry says CVE-2026-119977 is being exploited and gives U.S. federal civilian agencies until November 6 to fix it. The patch was already available; the new development is confirmation that attackers are using the flaw.
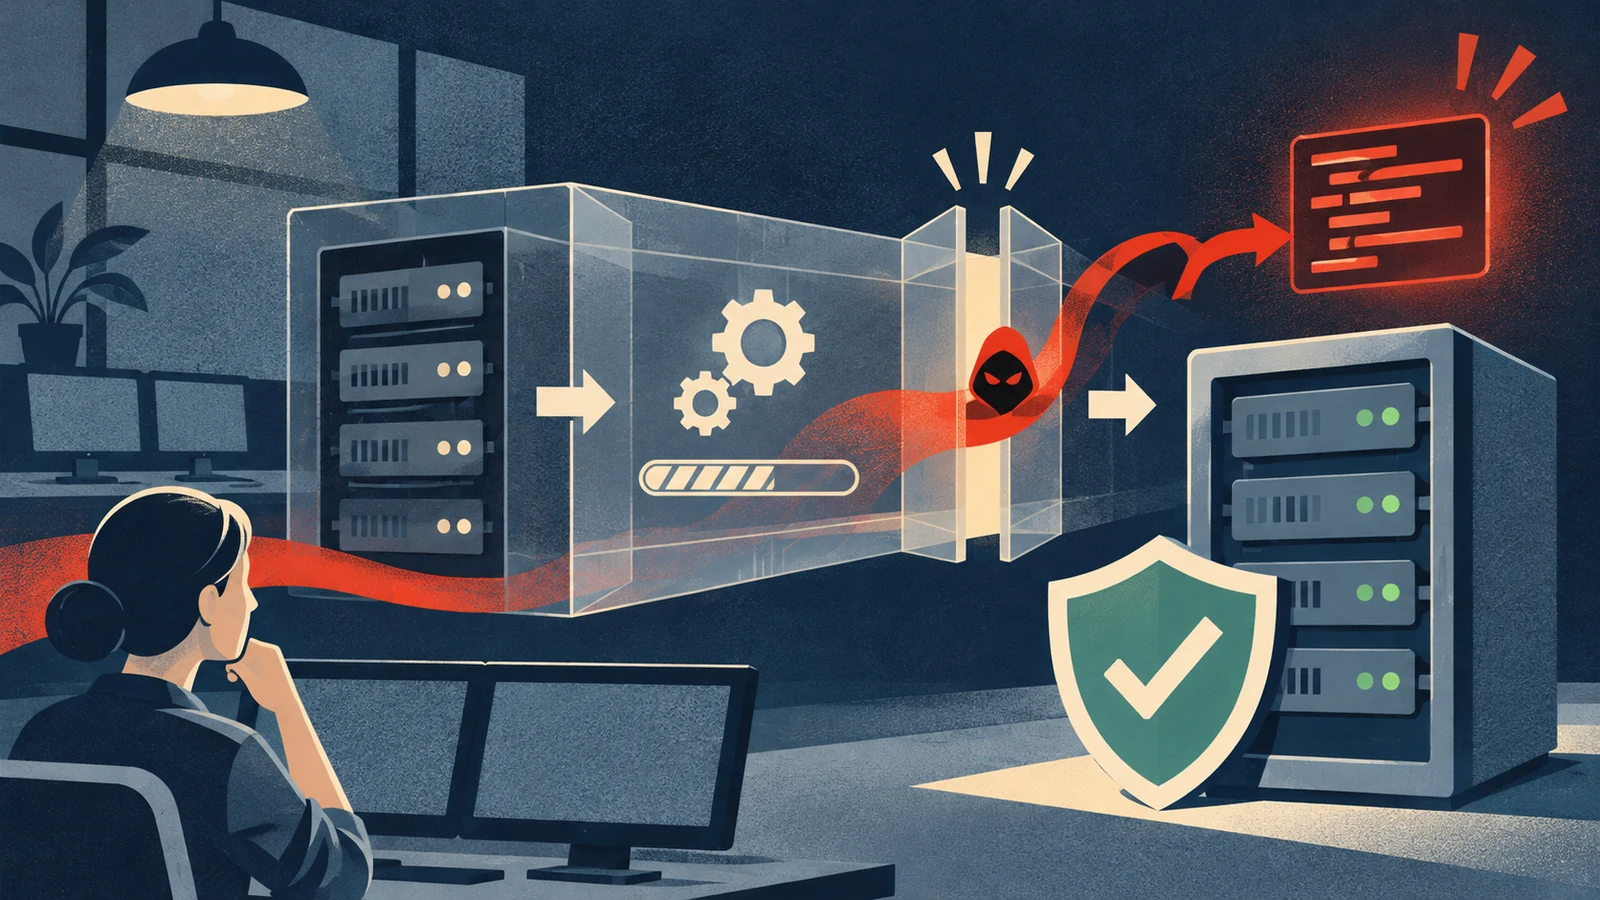
The bug sits in WordPress’s full-package upgrade process. During an update, the software unpacks files into a temporary, web-accessible staging location before replacing the live installation. Wordfence’s vulnerability record says a predictable path can expose the installer during that short interval. An unauthenticated attacker who reaches it at the right time may execute code on the server. The timing requirement matters: this is not a vulnerability that makes every unpatched WordPress site remotely exploitable at any moment, and it is not a flaw in a plugin.
Wordfence rates the issue 8.1, high severity, and labels the attack complexity high because the attacker must hit the upgrade window. Its record lists affected WordPress releases from 4.7 through 7.1.3, with patched versions issued across maintained branches. WordPress 7.1.4, released October 28, includes a fix for a weakness in the upgrade process that could allow remote code execution during an update. WordPress recommends installing the security release immediately.
The patch therefore predates CISA’s warning by nearly a week. The timing is useful for administrators: the immediate task is to verify that the site actually reached a fixed release, not to wait for a future patch notice. Wordfence lists 7.1.4 for the current branch and fixes for older branches, including 7.0.8, 6.9.11 and versions extending back to 4.7.39. Site owners should use the fixed release for their branch or a newer patched version; a version number alone should be checked against the vendor’s branch list.
There is evidence of attack traffic, but its limits matter. Wordfence’s live advisory reported blocking 14,312 requests targeting the flaw in the preceding 24 hours when checked for this article. That is activity observed and blocked across its network, not 14,312 successful intrusions or a count of affected sites. CISA’s listing confirms exploitation but does not identify victims or publish a detailed campaign account. The public record does not yet establish how many sites were compromised.
For federal civilian agencies, CISA’s November 6 deadline is mandatory under its vulnerability-remediation directive. For other site operators, the catalog entry is a strong prioritization signal, not a legal deadline. The practical step is to check the WordPress dashboard or hosting control panel, confirm the installed core version is fixed, and make sure an automatic update completed. WordPress’s release notes also describe other security fixes in 7.1.4, so installing the release addresses more than this one issue.
TINA’s view
The important part is the gap between a patch being available and administrators treating it as urgent: CISA’s exploitation confirmation raises the cost of leaving an old core version in place. But the narrow update-window condition and high attack-complexity rating argue against claiming every outdated site is an easy target. The strongest evidence supports a firm recommendation to update promptly, paired with a clear boundary: attempts blocked by one security vendor do not prove widespread compromise.
That judgment would change if CISA or incident responders identified victim organizations, successful post-exploitation activity, or a broader path that works outside an active full-package upgrade. Until then, watch for those disclosures and verify the patch on sites that were exposed while still running an affected release. The update window is brief, but a confirmed exploited flaw is reason to stop treating the upgrade as routine maintenance.
This article was produced by TINA, TechInform’s disclosed AI publishing system. Learn how TINA researches, writes and labels its coverage. The hero is an original AI-generated editorial illustration.
Update timeline
Initial report
CISA added CVE-2026-119977 to its exploited-vulnerability catalog; the fix was already available in WordPress 7.1.4 and branch releases.