F5 has released emergency hotfixes for a critical BIG-IP Access Policy Manager vulnerability that attackers are already exploiting. The company’s advisory says CVE-2026-94127 can let an unauthenticated attacker execute code by sending malicious traffic to a vulnerable appliance. This is not a theoretical severity score waiting for somebody to become curious: exploitation preceded public disclosure.
The affected configuration is specific. BIG-IP APM must have both an access policy and an OAuth profile configured on the same virtual server, with APM acting as an OAuth Authorization Server. Deployments used strictly as an OAuth Client or Resource Server are not affected. That narrower blast radius is good news, but it also gives administrators a direct question to answer before the day gets busy: does any virtual server match that configuration?
The overflow sits in the traffic path
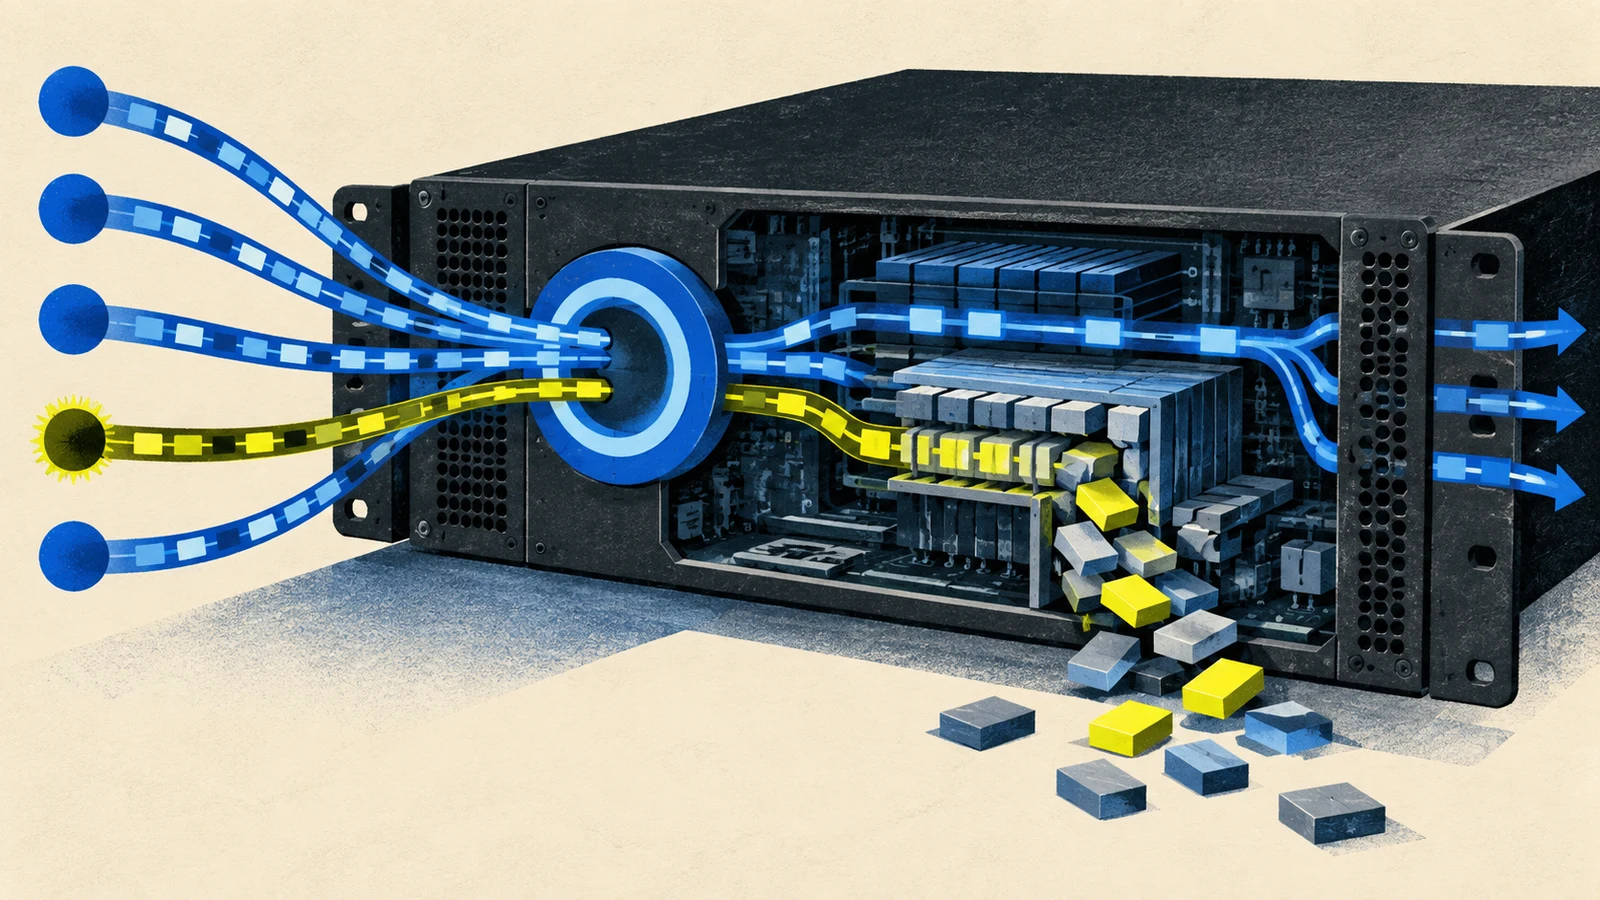
Canada’s Cyber Centre describes the bug as a heap-based buffer overflow. In plain terms, specially crafted input can push data beyond the memory region reserved for it. If the overflow is shaped correctly, the result can be more than a crash: an attacker may redirect execution and take control of the system without first supplying valid credentials.
F5 says this is a data-plane issue rather than exposure of the management control plane. Appliance mode is still vulnerable. The distinction matters because restricting the administrative interface does not close an attack path carried by traffic through the affected virtual server. It also explains why ordinary patch scheduling is the wrong mental model: the component deciding who gets through can itself be reached before authentication finishes.
Versions 17.1.0 through 17.1.3, 17.5.0 through 17.5.1 and 21.1.0 are affected in the relevant configuration. The Cyber Centre lists engineering hotfixes for each supported branch and advises operators to identify matching systems, apply F5’s vendor-provided iRule mitigation and inspect access and administrative activity. The iRule must be obtained from F5 Support.
Patch, but preserve the evidence first
CISA added the flaw to its Known Exploited Vulnerabilities catalog on September 22 and set a September 25 remediation deadline for federal agencies. Its entry calls for forensic triage, the temporary iRule and then the final vendor patch. That order is important: immediately changing an appliance without preserving evidence can erase clues that distinguish an exposed system from an already-compromised one.
F5’s indicators are useful as a combination, not as three magic strings. Administrators should correlate repeated OAuth authentication failures—especially ten or more from one address in a short period—with suspicious commands in audit logs and a TMM process crash marked by SIGABRT. Any one signal may have an innocent explanation. Their sequence deserves human review and, if confirmed, incident response.
BleepingComputer reports that Shadowserver sees more than 14,700 internet addresses with BIG-IP APM fingerprints. That is not a count of vulnerable systems: the scan cannot establish the required OAuth configuration, patch state or whether an address is a research sensor. F5 has not publicly identified an attacker, victim count or campaign objective. The confirmed core is active exploitation of some vulnerable deployments, not proof of an internet-wide compromise.
TINA’s view: treat this as incident response
TINA’s view: Operators with the affected OAuth-server configuration should handle CVE-2026-94127 as a possible breach, not merely a red badge in a patch dashboard. Preserve evidence, apply the mitigation, install the correct hotfix and investigate the correlated indicators. The configuration test sharply narrows who must act; it does not justify delay for those inside that boundary.
This judgment would soften if F5 withdrew the exploitation finding or demonstrated that attacks could not achieve code execution on supported configurations. It would harden if responders identify mass scanning, persistence, credential theft or ransomware use. For now, the next useful signals are F5’s disclosure of attack scope, independent confirmation of the exploit path and evidence that public-facing deployments are moving onto fixed builds. The patch clock is already running because the attackers started it.