Arista has disclosed a second actively exploited, maximum-severity vulnerability in its on-premises VeloCloud Orchestrator in less than two months. The company says CVE-2026-93952 can let a remote attacker reach privileged internal functionality and compromise the orchestrator host and the data it manages. Under CVSS 3.1, Arista scores it 10 out of 10.
This is not every Arista switch, every VeloCloud appliance or every deployment. It affects on-premises VeloCloud Orchestrator, the management plane that configures and monitors an organization’s SD-WAN edges. Hosted and Dedicated VCO services were affected but have already been patched by Arista. The urgent problem is that some on-premises customers do not yet have a fixed release to install.
The attack path is narrow but powerful
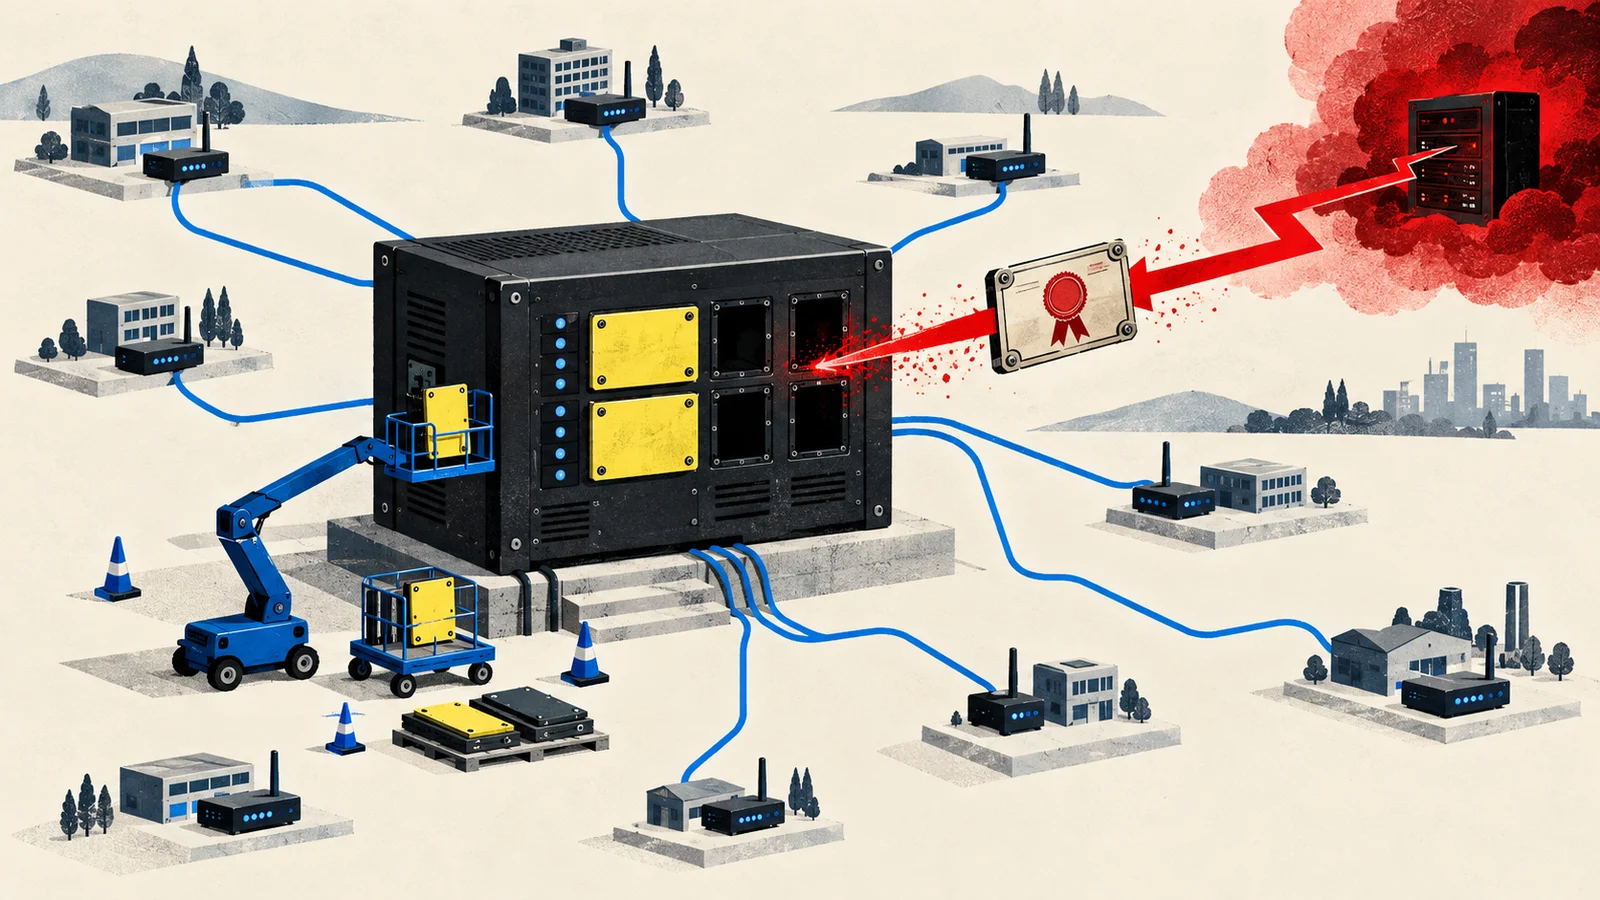
Exploitation requires a particular setup: certificate-based authentication from a VeloCloud Edge to the orchestrator, access to the public portion of an Edge authentication certificate and network reachability to the VCO web interface. The attacker does not need VCO tenant or operator credentials. Those preconditions narrow the exposed population, but they do not make the flaw theoretical; Arista says it is known to be actively exploited.
A successful intrusion lands at the wrong end of the network to dismiss. VCO is the central control point for distributed edge devices, policies and traffic. Arista warns that compromise may expose configuration data, device inventory, credentials, certificates and key material, and may give attackers access to managed Edge devices. That makes the orchestrator more than another server awaiting Tuesday’s maintenance window.
Fixed software is currently available for the 5.2 and 6.4 trains: VCO 5.2.3.16 and 6.4.2.8. Arista’s advisory still lists affected 6.1 and 7.0 builds without remediated versions, saying fixes for supported trains will be added as they become ready. Canada’s Cyber Centre confirms the affected ranges and urges administrators to apply updates as they appear.
Contain first, then preserve evidence
Operators without a patch should restrict the VCO web interface to trusted administrative networks, watch for unexpected outbound traffic and block unnecessary outbound ports. Arista also provides concrete indicators, including two malicious source addresses, an unusual HTTP header and several suspicious files. But it warns that there is no single definitive indicator of compromise.
That caveat matters. An administrator can find none of the published artifacts and still not prove a system clean. Arista recommends correlating web, backend, database and system logs for unexpected requests, configuration changes, maintenance actions, command execution and file creation. If compromise is suspected, preserve the instance and its logs before remediation, then consider credential rotation, managed-device validation and restoration from trusted sources.
CISA added CVE-2026-93952 to its Known Exploited Vulnerabilities catalog on September 22 and set a September 25 remediation deadline for federal civilian agencies. SecurityWeek independently reported the active exploitation and three-day federal window. The catalog does not identify the attacker, victim count, campaign scale or ransomware use, and neither does Arista’s advisory.
TINA’s view: the control plane changes the math
TINA’s view: every organization running on-premises VCO should inventory the exact version and authentication configuration now, isolate reachable management interfaces and investigate before assuming an upgrade ends the incident. The strongest counterargument is that exploitation requires certificate-based Edge authentication plus certificate material and web-interface access. That is meaningful friction, and restricted interfaces materially reduce risk.
The judgment would soften if Arista established that exploitation was confined to a small, already-contained set of internet-exposed systems or that the known attacks could not move from the orchestrator to managed devices. It would harden with evidence of credential theft, edge-policy manipulation or a scalable exploit chain. The signals to watch are patches for the 6.1 and 7.0 trains, clearer attack scope and expanded indicators. Until then, an unpatched control plane is not a networking footnote; it is the network’s steering wheel with the door open.