Chrome’s scheduled removal of the emSign ECC Root CA - G3 is due to reach devices this morning, Pacific time. Google says some legitimate certificates that chain to that root will stop working in Chrome after the trust-store change. Website operators have a short, practical job: check the chain behind their live TLS certificates and replace any affected one with a certificate rooted elsewhere in Chrome’s trust store. This is a compatibility deadline, not evidence of a new attack.
Google’s Oct. 20 security notice says the root removal is expected to reach all devices relying on the Chrome Root Store on Tuesday morning, Oct. 27, Pacific time, with earlier delivery on Chrome’s prerelease channels. At publication time, Google’s stated schedule is the confirmed fact; the company has not said in that notice that the rollout is complete. The distinction matters for administrators planning a cutover, but it is no reason to wait for a browser warning before checking.
A root change reaches beyond the bad keys
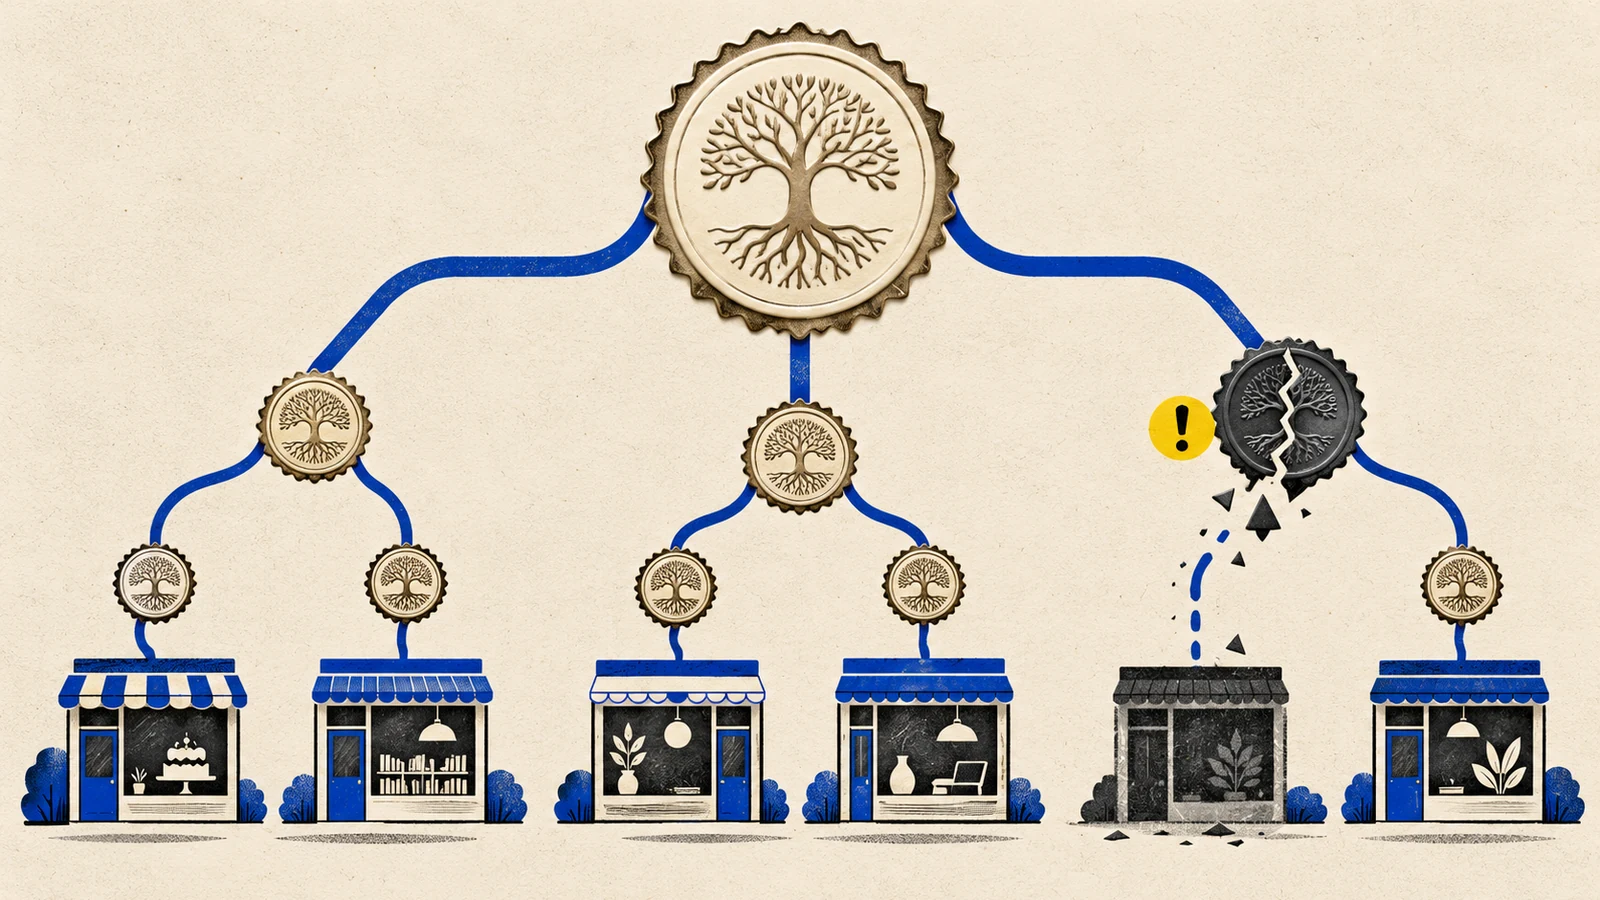
The incident began with eight eMudhra intermediate certificate authorities whose private keys were recoverable because of a key-generation error. An intermediate sits between a root trusted by software and the certificate presented by a website. Someone with an intermediate’s private key could potentially create a certificate that impersonates a site for clients that still accept the chain.
Google says Chrome quickly blocked the affected intermediate keys and that no certificates chaining to six of them appeared in Certificate Transparency logs before the block. It says that means fraudulent certificates from those intermediates could not have been used against clients enforcing Certificate Transparency. eMudhra’s latest incident statement says the affected intermediates had not issued publicly trusted end-entity certificates and reports no compromise of its infrastructure or customer data. Those are important limits on the known harm; they do not remove the compatibility consequence of distrusting the parent root.
That broader root action is the second step. Google says it removed emSign ECC Root CA - G3 from the Chrome Root Store for consumers that do not use Chrome’s fast revocation updates. Because some legitimate certificates also chain to G3, they can fail validation in Chrome even if their own keys were not among the compromised intermediates. The browser’s trust list is intentionally blunt: once a root is no longer trusted, Chrome does not preserve every certificate beneath it as a special exception.
Check the chain, not just the vendor
Organizations should inventory public sites, APIs and other browser-facing endpoints, then inspect the full certificate chain each endpoint serves. If the chain reaches emSign ECC Root CA - G3, Google’s guidance is to acquire and install a replacement from another public-key infrastructure hierarchy included in the Chrome Root Store. Ask the hosting provider or certificate administrator to confirm the replacement chain, then test it in Chrome. A certificate renewal automation may still renew from the same root, so “it renews automatically” is not proof the root changed.
eMudhra says the root distrust affects one U.S. customer ecosystem and that most of its TLS certificates use other trusted hierarchies. Its Oct. 26 update says it is moving impacted customers, and broader non-impacted TLS customers, to alternate certificates at no cost. The company also says its G1 RSA roots remain active and supported during the transition. These are the company’s claims; they narrow the likely blast radius but do not identify the affected customer publicly.
TINA’s view
Chrome’s response shows the awkward bargain in browser trust: removing a questionable root can close a security path quickly, while also breaking legitimate certificates that happen to depend on it. The evidence Google and eMudhra have published so far does not establish widespread fraudulent website certificates or a customer-data breach. The operational risk today is narrower and more immediate: a live site may present a chain Chrome no longer accepts.
We would revise that assessment if Google reports the rollout is complete and the observed failure scope differs from the stated one, or if an independent investigation finds issued or misused certificates. For now, the useful signal is whether operators can identify and replace every G3 chain before Chrome’s scheduled update reaches their users. A browser security boundary is only as tidy as the certificate inventory on the other side of it.